

{origin}/oauth, for clients that act on behalf of a user.
Personal access tokens
For scripts, backend services, and anything else calling the REST API directly, use a personal access token (PAT):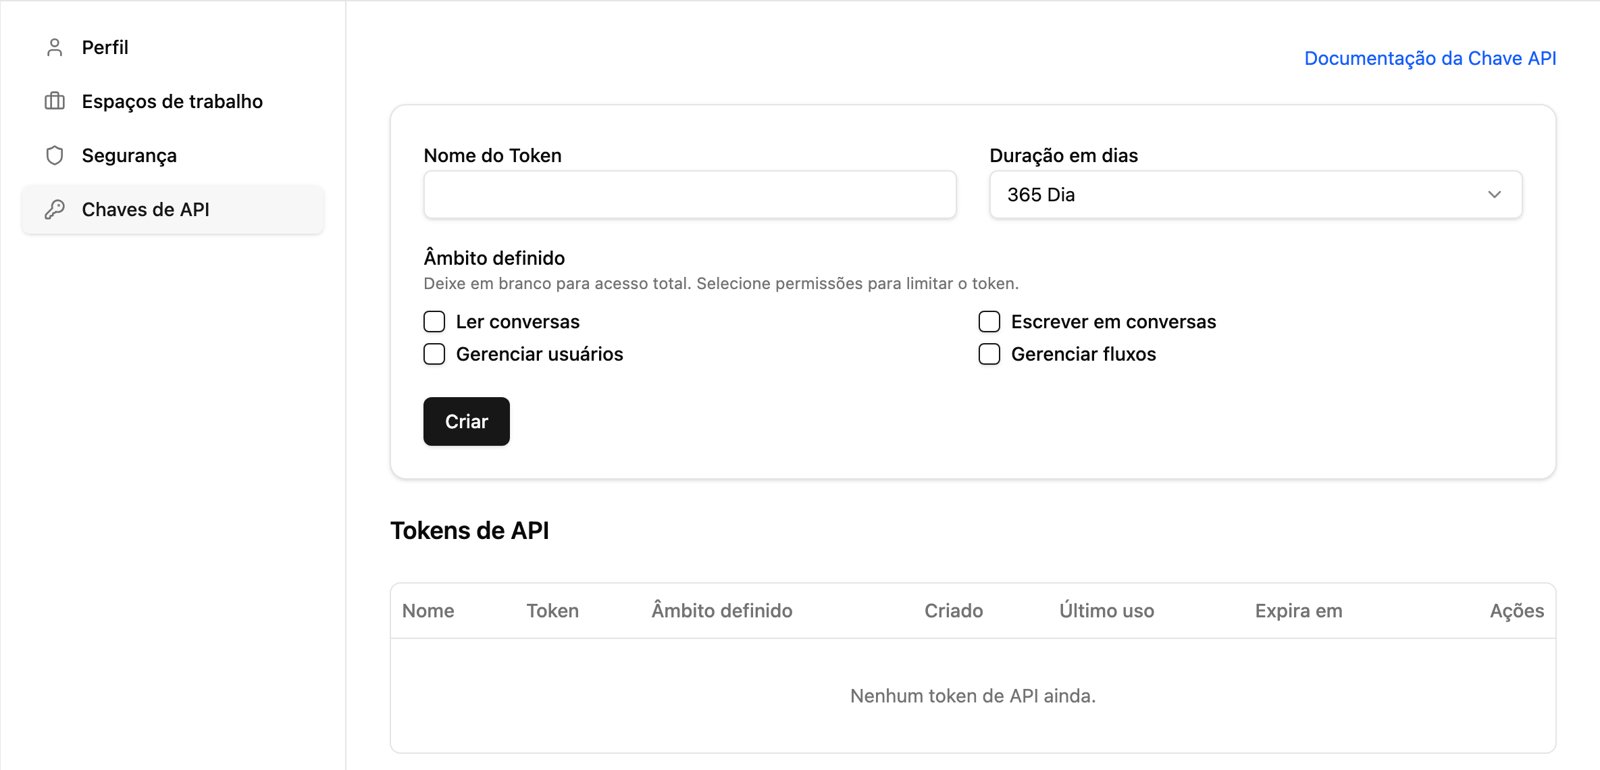
OAuth 2.0 (third-party apps)
Use the authorization-code + PKCE flow for clients that act on behalf of a user.Discovery
Clients discover the authorization server via standard metadata documents:
The MCP endpoint returns
401 with a WWW-Authenticate header, so spec-compliant
MCP clients bootstrap the OAuth flow automatically.
Flow
GET /oauth/authorizewithresponse_type=code,client_id,redirect_uri,code_challenge,code_challenge_method=S256, andstate.- The user authenticates and approves; iZap redirects back with
code. POST /oauth/tokenwithgrant_type=authorization_code,code,redirect_uri, andcode_verifier→ returns anaccess_token(JWT) and arefresh_token.
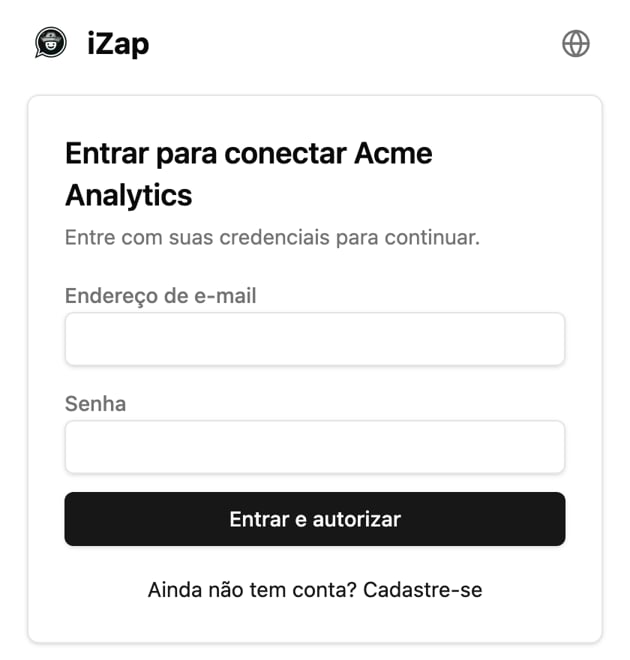
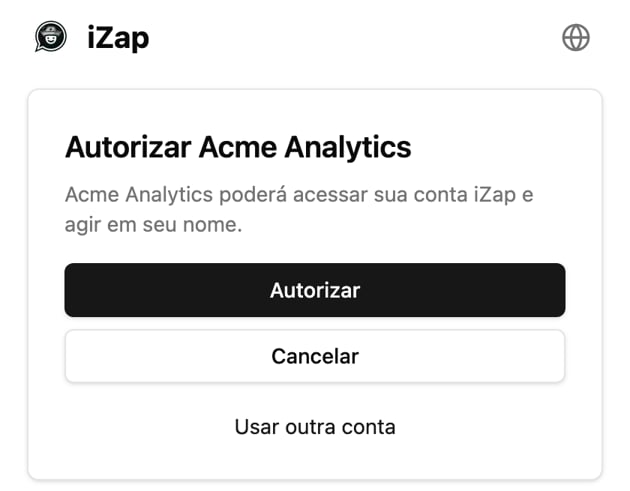
POST /oauth/register. Refresh an expired
token with grant_type=refresh_token.
Token notes
- Every token — personal access token or OAuth access token — is a secret. Read it from an environment variable or secret manager, never hardcode it.
- A personal access token does not expire on its own; it is valid until you revoke it from the dashboard.
- OAuth access tokens expire. Use the refresh grant when a request returns
401.